Hire DevSecOps Engineers for US Platform Teams
· Typical time to first merge-blocking security gate: 12 to 15 business days
Hire DevSecOps engineers through Siblings Software when your US product team needs pipeline security talent embedded in your ceremonies without a six-month search for AppSec plus CI/CD hybrids. We coordinate delivery from Miami with full-time engineers in Latin America who overlap US Eastern business hours. You get live vetting on merge-blocking gates, SBOM paths, signing verification, and whether you need one senior, a pair, or a small pod before you sign paperwork.
This page covers weekly responsibilities, buyer scenarios, vetting signals, engagement models and monthly bands, hiring timelines, tradeoffs versus freelancers and in-house hiring, illustrative scenarios, risks we contract around, and when DevSecOps services fits better than individual seats. This lane is not hire DevOps engineers for general CI/CD throughput, not hire SRE engineers for on-call reliability alone, and not hire platform engineers for golden paths only. For the parent category see staff augmentation. For timezone context read nearshore developer hiring. For full delivery ownership compare DevOps engineering or AI code security.
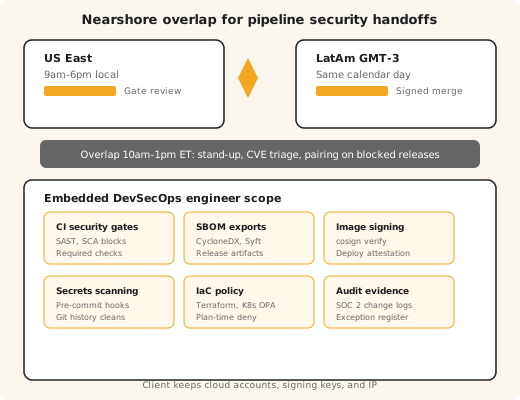
Most US East clients get four to eight hours of same-calendar-day overlap for gate review, CVE triage, and release pairing.
Prefer numbers before a call? Jump to monthly pricing bands for embedded seniors, pairs, and small pods.
When US companies hire DevSecOps engineers through us
Four situations cover most discovery calls; yours may combine two.
Scans that report but never block merges
GitHub Advanced Security or Snyk dashboards fill up while main still merges on green unit tests only. Staff aug adds engineers who edit workflow YAML and policy bundles while you close a US full-time hire, or becomes steady state when AppSec hybrids are scarce in your market.
Unsigned containers still reach production
Production trusts mutable tags, cosign keys lack a custodian, and hotfix branches bypass required checks. You need gate fixes and an audit trail without freezing the roadmap.
SOC 2 or ISO change evidence stuck in spreadsheets
Auditors want traceability from commit to signed artifact. Embedded engineers wire evidence folders aligned with the OWASP Top Ten and SLSA without pausing feature work.
Enterprise security questionnaires blocking deals
Prospects send SIG or CAIQ packets while pipelines still allow skip-scan deploys. Engineers embed to add merge-blocking gates, SBOM exports, and sample evidence packs sales can attach.
If none of these match, say so on the call. We turn down engagements when another delivery lane is a better fit.
What DevSecOps engineers do in client teams
Pipeline gates, supply chain attestation, and evidence packs, not a generic security checklist.
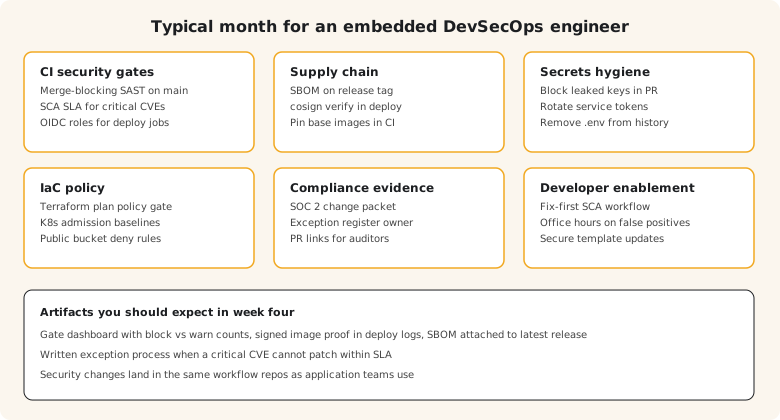
In a typical month an embedded engineer might turn a warning-only SCA step into a merge blocker on main, attach CycloneDX SBOMs to release tags, verify cosign signatures in deploy pipelines, add Checkov gates beside Terraform plans, refresh a SOC 2 evidence folder after a control change, and document who approves gate exceptions. The diagram below is a schematic of those parallel tracks. Your mix depends on audit pressure, repository count, and how mature your Secure Delivery Pipeline Readiness Gate answers are today.
CI security gates and policy
SAST, SCA, and container scan severity thresholds with named owners, required checks on main and release branches, and exception workflows your security team can audit. We align with your GitHub or GitLab workflows rather than parallel spreadsheets.
Supply chain attestation
SBOM generation on promoted builds, image signing with cosign or Sigstore, verification in deploy pipelines, and attestations mapped to SLSA levels you can explain to customers. For vendor-owned programs see DevSecOps services.
Secrets and IaC scanning
Gitleaks or equivalent on pull requests, Terraform and Kubernetes policy checks in the same merge queue as application code, and routing alerts to engineers who can rotate credentials within one business day.
Compliance evidence and enablement
Evidence folders mapped to SOC 2 change-management controls, sample PR check exports, and short enablement sessions so product teams understand why a gate blocked their merge. Runtime detection and on-call work belongs under hire SRE engineers; copilot secret patterns under AI code security.
How Siblings vets DevSecOps engineers
Resume screens miss the failures that show up in week three of an audit window.
Before anyone joins your stand-up we run a written scoping answer on a small CI gate design question, then a ninety-minute live session on production-shaped pipeline code. We check communication in English, how candidates explain tradeoffs to a platform lead, and whether they reach for gate evidence before recommending another dashboard. Red flags we screen out: candidates who treat security as a ticket queue outside engineering, who cannot read your workflow YAML, or who need a greenfield demo to show value in week one.
We align practice with the GitHub code security documentation and your existing controls, not audit-only slide decks.
Secure Delivery Pipeline Readiness Gate (four signals)
A lightweight decision model you can reuse even if you never hire us.
Before we shortlist, we walk through four signals with your platform or security lead on a thirty-minute call. The same gate appears on our DevSecOps services page because buyers confuse staff aug and vendor-owned programs when gate ownership is unclear.
- 1. CI security gate ownership. Is there a named owner who merges SAST, SCA, and container scan policy and enforces required checks on main?
- 2. Supply chain attestation. Do release artifacts ship with SBOM exports and image signing verified at deploy time?
- 3. Secrets and IaC scanning. Do pre-commit and pipeline checks catch leaked keys and Terraform drift before merge?
- 4. Compliance evidence path. Can SOC 2 or ISO controls map to automated checks auditors trust?
Your platform lead validates the shape on the discovery call. We match the bench to that profile rather than sending a generic DevOps resume with security buzzwords.
Engagement models and monthly ranges
Published bands beat hidden pricing when you are budgeting a quarter.
The point inside each band moves with seniority, stakeholder-facing English depth, and rare skills such as regulated healthcare pipelines or multi-cluster signing ceremonies.
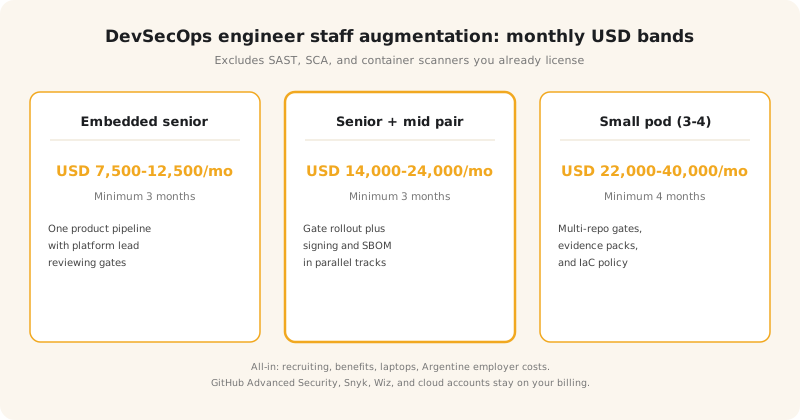
Embedded senior
One senior in your ceremonies and code review rotation. Strong when your engineering culture is healthy and you need pipeline security depth without re-teaching basics.
Monthly: USD 7,500 to 12,500. Minimum: three months.
Senior + mid pair
The senior sets gate policy; the mid-level absorbs tickets once context lands, usually by week four. Common when you want sustained velocity across multiple repositories.
Monthly: USD 14,000 to 24,000. Minimum: three months.
Small pod (three to four engineers)
Covers vacations internally and can split between CI gate rollout and a parallel signing or evidence track under your platform lead. If you want a vendor-owned program instead, DevSecOps services is usually the better commercial shape.
Monthly: USD 22,000 to 40,000. Minimum: four months.
Figures include recruiting, benefits, laptops, and employer costs. Infra, security SaaS, and signing KMS stay on your accounts.
Hiring timeline: intro call to first merge-blocking gate
Short steps that end with you meeting the person who will commit.
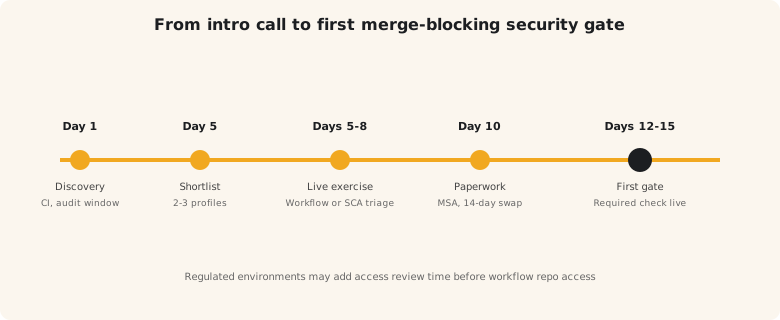
- Discovery (day 1). Stack, team topology, risk areas, hard nos on tooling, budget envelope. We say no on the call when we are the wrong partner.
- Shortlist (by day 5). Two or three profiles with workflow examples where available and a written answer to a scoped CI gate design question.
- Live pair (days 5 to 8). Ninety minutes with your platform lead on a sanitised slice of work: flaky scan step, bypassed required check, or cosign verification gap.
- Paperwork (days 8 to 10). Master services agreement, monthly statement of work, fourteen-day swap clause in plain language.
- First merge-blocking gate (days 12 to 15). Onboarding pairs on a small production-safe gate change so you see integration speed, not slide decks.
Embedded DevSecOps versus freelancer, in-house, or large offshore bench
Each option wins sometimes; pretending otherwise wastes your time.
Freelance marketplaces
Win on narrow spikes under about 80 hours. Lose on continuity and queue hygiene when the incentive is ticket throughput, not gate ownership.
In-house hiring in the US
Wins on five-year ownership. Loses on funnel length and regret cost when the hire misses at month six while audit deadlines continue.
Large offshore agencies
Win when you truly need ten mid-level ticket takers with a PM layer. Lose when the engineer in the interview is not the engineer in your workflow repos.
Where we sit
Small senior bench, Miami-led coordination, Latin America overlap with US Eastern hours, fifteen-day notice after the minimum, and the person you interview is the person who commits.
Illustrative scenarios (composites)
Shapes we have shipped multiple times. Details blended to protect clients. Not named case studies with verified metrics.
Health API microservices sprawl
US B2B health data platform with dozens of GitHub Actions workflows and inconsistent scan configs. Embedded senior plus mid pair, required checks on main, SBOM on top deploy paths. Product kept shipping while security risk moved in controlled slices. Related fictional program shape: Clearwater Health API on our DevSecOps services page.
Payments renewals with SIG questionnaires
US payments SaaS with mutable tags in production and two enterprise renewals pending. Six-week engagement: cosign verification in GitOps, evidence sample mapped to change-management controls, gitleaks on active repos. Sales answered questionnaires without a platform rewrite.
Example engagement
Published proof: ISO 27001 compliance SaaS on AWS
Anonymised client under NDA. Facts verified on our case study page.
Context. European compliance SaaS team needed merge-blocking container scans and audit-friendly change evidence while migrating to AWS Fargate.
What we did. Embedded DevSecOps and platform engineers enforced Trivy gates on promoted images, wired evidence exports, and paired with the client security lead on control mapping.
Why it matters for hiring. The same engineers can embed through staff augmentation when you already own gate policy and need seats inside your ceremonies. Read the full ISO 27001 compliance SaaS case study.
At a glance
Model: DevSecOps plus platform delivery
Focus: CI gates, AWS, ISO 27001
Risks of embedding DevSecOps engineers and how we reduce them
Honest controls beat vague assurance language.
Interview star, week-three stall
Mitigation: pair on real pipeline code, fourteen-day swap window, explicit day-fourteen check-in with your lead.
Shadow contractor behavior
Mitigation: our engineer joins your reviews both directions, not only outbound PRs, and works only on your backlog.
Knowledge leaves with the engagement
Mitigation: ADRs for non-obvious calls, runbooks for jobs we touch, handover notes at month three even if you extend.
Vanity refactors instead of metrics
Mitigation: monthly scorecard on numbers your leadership tracks: blocked critical findings, unsigned deploy attempts, mean time to rotate leaked secrets, evidence pack freshness.
Why Siblings for DevSecOps staff augmentation
Miami headquarters, nearshore engineering depth, direct access to leadership.
Since 2014
US-facing delivery
Platform, product, and security engagements from Miami
250+
Engagements delivered
CI gates, SBOM, signing, and compliance evidence work
US hours
Nearshore overlap
Same-calendar-day pairing with US Eastern leads
Founders still review new DevSecOps staff aug engagements, and engineers talk to clients without a telephone game of account managers. That is why the process above stays short.
Reviewed by Javier Uanini, Founder & CEO, Siblings Software. Technical discovery on DevSecOps staff augmentation engagements, pricing bands, and fit decisions.
Frequently Asked Questions
US platform, security, and compliance leads hire DevSecOps engineers through Siblings when merge-blocking CI gates, SBOM exports, or SOC 2 change evidence lag product velocity. We embed senior pipeline security engineers in your ceremonies from Miami-coordinated nearshore delivery. You keep repositories, signing keys, and IP. We staff recruiting, payroll, and benefits.
Budget USD 7,500 to 12,500 per month all-in for one senior DevSecOps engineer, USD 14,000 to 24,000 for a senior plus mid pair, and USD 22,000 to 40,000 for a three-to-four person pod sharing pipeline context. Figures include recruiting and employer costs and exclude your cloud accounts, security scanner licenses, and signing infrastructure.
Most US clients reach a first merge-blocking gate in 12 to 15 business days after discovery: shortlist by day five, live pipeline exercise by day eight, paperwork by day ten, then onboarding with your platform or security lead. Regulated environments may take longer when access reviews apply.
We start with a written answer to a scoped CI gate design question, then run a ninety-minute live session on production-shaped workflow code: advisory-only SCA, unsigned images in GitOps, or Terraform policy checks bypassed on hotfix branches. We align shortlists with the Secure Delivery Pipeline Readiness Gate on gate ownership, supply chain attestation, secrets and IaC scanning, and compliance evidence paths.
One senior fits a single repository family with a platform lead who reviews every policy change. A pod fits parallel tracks: CI gate rollout, cosign hardening, and SOC 2 evidence refresh at the same time, plus vacation coverage during audit windows. For vendor-owned programs compare DevSecOps services.
DevSecOps staff augmentation embeds pipeline security engineers in your rituals and backlog. Hire DevOps engineers covers broader CI/CD and cluster operations. DevSecOps services delivers a vendor-owned secure delivery program when gate ownership is still undefined. We say no on the discovery call when another lane fits better.
We replace the engineer at no placement fee during the first fourteen days with reasonable handover overlap. After that, either side may exit with fifteen days notice once the minimum term is met. We check fit with your platform lead on day fourteen.
Our standards for DevSecOps work
What we hold ourselves to once embedded.
- Gates before exceptions. Merge-blocking policy before ad-hoc waivers on production paths.
- Artifacts you can attest. SBOMs, signatures, and promotion logs documented for auditors.
- Findings you can route. Scan output lands where engineers rotate secrets, not a shared mailbox.
- Gates with owners. Severities, exception approvers, and break-glass paths assigned, not implied.
- Policies versioned. Workflow and policy bundle changes tagged in release notes with evidence linked.
- Written artifacts. Runbooks for key rotation, gate exception logs in PR templates, rollback notes for signing changes.
Contact Siblings Software
Describe pipelines, gate maturity, and team topology. We reply within one business day, or tell you we are not the right partner.