DevSecOps Services for Secure Software Delivery
DevSecOps services from Siblings Software help US CISOs, VP Engineering, and platform directors wire security into delivery without turning every release into a review meeting. This page explains merge-blocking CI gates, SBOM exports on promoted builds, signed container images verified at deploy time, secrets and Terraform scanning in the same pull request path as application tests, and SOC 2 change evidence your auditors can follow. You can evaluate our Secure Delivery Pipeline Readiness Gate, typical eight to fourteen week programs, squad composition, pricing bands, risks, and how outsourced delivery compares with staff augmentation or in-house hiring.
We coordinate from Miami with nearshore engineering depth in Latin America when you want same-day pairing on blocked releases, signing ceremonies, or customer security questionnaires. Pipeline reliability and deploy frequency stay under DevOps engineering. Golden paths and developer portals stay under platform engineering. LLM-specific guardrails stay under AI code security. When you only need one senior engineer inside your squad, see hire DevOps engineers.
Controls align with the OWASP Top Ten, the SLSA specification, and GitHub code security documentation your teams already cite. Service decomposition and API hardening pair with microservices development when blast radius is the concern. Browse all services or compare nearshore development if procurement is weighing delivery regions.
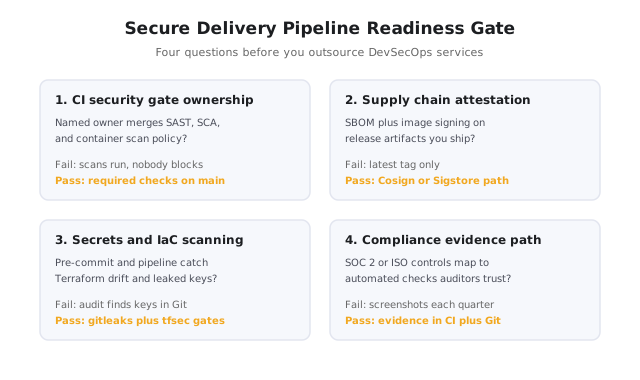
Use the readiness gate in discovery: if gate owners or signing custodians are undefined, document ownership before changing production workflows.
What the Service Covers
Outsourced DevSecOps is the cross-functional work of making secure delivery repeatable. A typical program baselines pipelines and artifact flows, runs the Secure Delivery Pipeline Readiness Gate, defines severity thresholds and exception owners, enforces scans and policy checks in CI, generates SBOMs and signed images on promoted builds, wires Terraform and Kubernetes checks into the same merge queue as application code, and hands off evidence templates compliance can reuse each quarter.
That differs from DevOps engineering, which optimizes deploy frequency and reliability rather than attestation and audit trails. DevSecOps optimizes merge-blocking clarity, supply chain provenance, and evidence that survives enterprise questionnaires. We pair with QA automation services when security checks belong beside functional suites, and with project-based outsourcing for a first hardening wave before a dedicated development team retainer for gate maintenance.
Quality gates follow what audit and customer security teams expect: no promotion of unsigned images to production, documented break-glass for critical hotfixes, and tabletop exercises on key compromise before SOC 2 fieldwork.
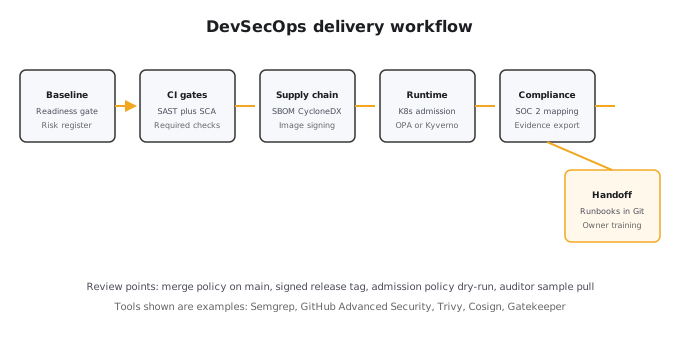
Security should not discover critical findings only after a tag reaches production. The workflow keeps prevention in pull requests and deploy verification on the same path engineering already uses.
Who It Is For
Platform and security leaders at B2B SaaS, health data, and fintech companies where GitHub or GitLab pipelines ship daily but findings still live in dashboards nobody merges. Enterprise customers ask for SBOMs and change evidence you cannot assemble in a week. If nobody can name who approves a pipeline exception within one business day, you are the audience.
Regulated health and data platforms
API products under HIPAA or SOC 2 where customers expect signed artifacts, access logs, and change tickets tied to production deploys.
Fintech and payments
Separate production and audit pipelines need consistent gates, secret scanning, and evidence packs for internal control reviews.
Multi-repo product engineering
Dozens of services on GitHub Actions or GitLab CI where each team invented a different scan configuration and security cannot see aggregate risk.
Kubernetes and container estates
Clusters pulling unsigned images, mutable tags in production, and Helm charts nobody scans before promotion.
Teams facing customer security reviews
Enterprise procurement sends SIG or CAIQ questionnaires while hotfix branches still allow skip-scan deploys.
After a shelfware security rollout
A SAST license went enterprise-wide but merge rates did not change. You need delivery that wires gates, not another dashboard seat.
Typical Project Scenarios
Six situations we hear on US discovery calls. Each maps to a bounded DevSecOps wave scoped in the first week after the Secure Delivery Pipeline Readiness Gate.
Standardize CI gates after microservice sprawl
Engineering added repositories faster than security could standardize workflows. We define severity thresholds, enforce scans in required checks, and backfill SBOM generation on the top deploy paths before the next customer audit.
Sign container images and verify at deploy
Production still trusts mutable tags. We implement cosign or equivalent signing, store public keys in your KMS, and wire verification into GitOps deploy pipelines with rollback notes coordinated with your platform team.
Scan Terraform and Kubernetes before merge
Infrastructure drift creates findings application scans never see. We add Checkov, tfsec, or Conftest policies aligned to your landing zone, merged through the same review path platform already uses.
Route secret findings to engineers who can rotate
Alerts land in a shared mailbox. We connect GitHub Advanced Security or GitLab secret detection to Slack routing, name custodians, and rehearse revocation within one business day.
Build SOC 2 change evidence from pipelines
Auditors want proof that production changes map to approved pull requests. We export check summaries, link tickets, and package sample releases aligned to CC8-style controls.
Harden APIs without pausing the roadmap
Customer contracts add mTLS and scope reviews mid-quarter. We coordinate boundary tests with microservices development and QA automation services so gates augment delivery instead of blocking it.
How Delivery Works
Six phases, usually eight to fourteen weeks for a first secure delivery program with enforced gates, signed release artifacts, IaC policy checks, compliance evidence samples, and paired handoff documentation. Tabletop exercises on signing key compromise are standard when customers ask for supply chain attestations.
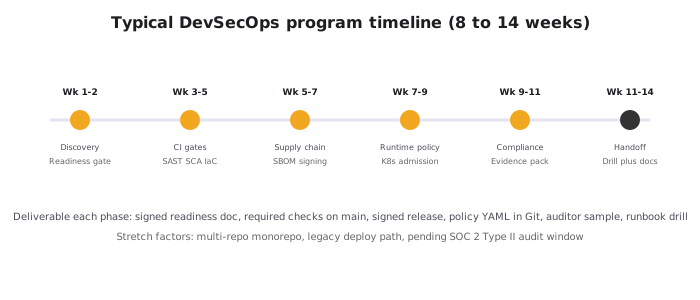
Discovery inventories repositories, pipelines, and artifact registries, runs the Secure Delivery Pipeline Readiness Gate, and documents gate owners, signing custodians, and evidence gaps.
Gate design delivers severity matrices, required checks per branch, exception workflows security signs, and policy-as-code bundles your platform team merges like application code.
Supply chain wave implements SBOM generation on promoted builds, image signing, provenance metadata aligned with SLSA targets, and verification hooks validated in staging before production promotion rules change.
IaC and secrets adds Terraform, Helm, and Kubernetes scans, secret detection on push, and rotation runbooks wired to the same on-call paths as production incidents.
Evidence and reporting configures export jobs, sample SOC 2 folders, and customer questionnaire templates reconciled to actual pipeline outputs.
Handoff includes runbooks for onboarding a new service, rotating keys, and regenerating attestations. Paired weeks let your team merge changes under our review before we step down to advisory hours or a retainer.
Team Composition
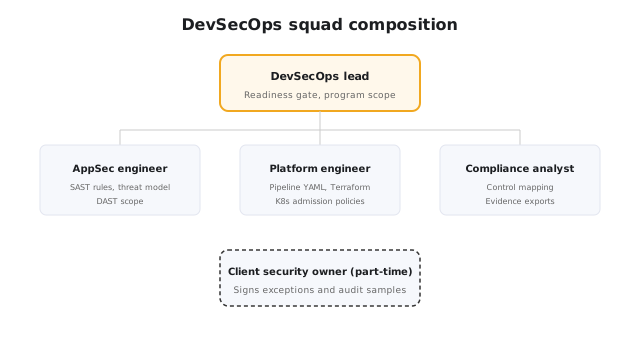
A four- to five-person squad is the usual shape for a first DevSecOps program. The DevSecOps lead who owns the readiness gate, customer evidence narratives, and exception policy and the platform engineer who merges workflow and signing changes are the two roles that determine whether auditors trust the next release sample.
Typical roster: DevSecOps lead, application security engineer for threat modeling and gate tuning, platform engineer for pipelines and IaC, part-time compliance or GRC owner from your side who signs evidence templates, and optional QA liaison when security checks integrate with functional automation. For ongoing gate maintenance after wave one, the same squad can run as a dedicated development team on a monthly retainer. For a single senior engineer inside your org, staff augmentation is the better fit.
Project, dedicated team, or staff augmentation depending on how much of the secure delivery roadmap you want us to own.
Pricing and Engagement Models
Project-based
Fixed scope for a bounded secure delivery program: readiness gate, CI gate rollout, supply chain signing, IaC and secret scanning, evidence samples, and handoff documentation. Typical duration eight to fourteen weeks. Published bands run USD 30,000 to USD 115,000 after discovery, depending on repository count, multi-cloud scope, and audit reporting depth.
Dedicated team
Ongoing squad owning gate tuning, signing key lifecycle, SBOM storage hygiene, and quarterly evidence refresh. USD 20,000 to USD 55,000 per month for four to six people depending on seniority mix and pipeline surface area.
Staff augmentation
Embed one or two senior DevOps engineers with security depth when you already own the program and need hands on workflow YAML, policy bundles, or cosign modules. USD 7,500 to USD 12,500 per month per senior engineer on published brackets.
Compared With In-House Hiring, Freelancers, and Large Consultancies
Outsource when
- You need merge-blocking gates, signed artifacts, and audit evidence in one or two quarters, not after a long search for a rare AppSec plus platform hybrid.
- Security owns dashboards but engineering never merges findings.
- Leadership wants a third party to document the Secure Delivery Pipeline Readiness Gate before customer diligence on your SDLC.
- Enterprise questionnaires arrive every quarter because nobody owns an evidence regeneration playbook.
Keep it in-house when
- You already run weekly secure delivery reviews, gate bypass rates near zero, and only need a short spike on one repository.
- Software is internal-only with no customer audit pressure and no plan to sell into regulated industries next year.
- A vendor delivers PDF reports your engineers are not allowed to merge into pipelines.
Freelancers can tune one pipeline quickly but rarely stay for signing key custody or SOC 2 sample packs at board level. A blended US plus nearshore squad often lands faster than hiring the same mix locally in major US metros. Browse case studies for how we work with product teams.
Illustrative Scenario: Clearwater Health API
Composite illustrative scenario only. Not a published client case study. No performance metrics are claimed.
The situation
Clearwater Health API is a fictional B2B health data platform connecting payers to provider systems. GitHub Actions deploys dozens of microservices daily while security still runs quarterly manual reviews. Container images pull from a shared registry without verification, Terraform plans skip policy checks on hotfix branches, and SOC 2 auditors asked for change evidence the team cannot export from CI.
Leadership approved a DevSecOps program before renewing two enterprise contracts. They need the Secure Delivery Pipeline Readiness Gate passed, required checks on main and release branches, cosign verification in Kubernetes, and sample evidence folders mapped to change-management controls before the next customer security summit.
What we would deliver
A twelve-week program with a five-person squad: DevSecOps lead, application security engineer, platform engineer, part-time GRC analyst for evidence mapping, and a security owner from the client side. Eastern Time working sessions during gate rollouts and signing key ceremonies with the US platform lead.
- Secure Delivery Pipeline Readiness Gate documenting CI gate owners, supply chain attestation gaps, secrets and IaC scan coverage, and the compliance evidence path signed by security and platform.
- Reusable workflow modules with merge-blocking SAST, dependency, and secret scans on protected branches.
- SBOM generation on release tags and cosign-signed images verified in Argo CD, coordinated with DevOps engineering promotion rules.
- Terraform and Helm policy packs with exception workflows security approves in writing.
- SOC 2 sample change packets linking pull requests, checks, and tickets for three production releases.
In a scenario like this, the win is predictable secure delivery: engineers merge fixes like product work, customers receive attestations with releases, and leadership enters diligence with evidence already in the repository.
Risks and Mitigation
Gates block every release until noise overwhelms bypass culture. Teams disable checks after false positives spike. Mitigation: tune severities on historical findings, staged enforcement, and exception owners security signs.
Signing keys become a single-person dependency. Mitigation: dual custodians, documented ceremonies, and quarterly rotation drills in staging.
SBOM storage fills with unreadable JSON nobody consumes. Mitigation: attach SBOMs to release objects customers already download and automate retention aligned to contract language.
IaC scans fight platform templates. Mitigation: policy packs owned by platform, exceptions time-boxed, and findings routed like application defects.
Evidence packs rot when pipelines change. Mitigation: regenerate samples each quarter and tie updates to the same change tickets as workflow edits.
Microservice boundaries hide auth gaps. Mitigation: pair service reviews with microservices development and threat modeling workshops before new public APIs launch.
Questions buyers ask before the first discovery call
Frequently Asked Questions
Staff augmentation embeds one or two security-minded engineers inside your team on your backlog. Outsourced DevSecOps services deliver a governed program: pipeline security gates with named owners, supply chain attestation for images and dependencies, secrets and IaC scanning merged as engineering work, and compliance evidence packs auditors can trace. You still own repositories, cloud accounts, and IP. Choose staff augmentation when you already run secure delivery rituals and need extra hands. Choose this page when releases ship without consistent gates, SBOM exports are missing, and nobody can produce SOC 2 change evidence within one sprint.
We work across GitHub Actions, GitLab CI, Azure DevOps, Jenkins, and Argo CD style GitOps flows on AWS, Azure, and Google Cloud. Common tooling includes SAST and dependency scanners your team already licenses, OPA or Conftest for policy gates, cosign or Notary for image signing, Syft or CycloneDX for SBOM generation, and secret scanners wired to the same pull request path as unit tests. We align controls with OWASP Top Ten categories, SLSA build levels your risk team targets, and GitHub code security documentation when that is your source of truth.
Discovery documents the Secure Delivery Pipeline Readiness Gate: CI gate ownership, supply chain attestation, secrets and IaC scanning, and a compliance evidence path. Delivery includes merge-blocking checks for critical findings, SBOM generation on release artifacts, signed container images with verification in deploy pipelines, Terraform and Kubernetes policy scans through the same review path as application code, and evidence folders mapped to SOC 2 change-management controls. Runbooks name who approves exceptions and how to regenerate attestations after a key rotation.
Eight to fourteen weeks is typical for a first program: two weeks on baseline and readiness gate, four to eight weeks on gate rollout, supply chain signing, and IaC policy enforcement, two to four weeks on evidence packaging, tabletop exercises, and paired handoff. Timelines stretch when pipelines are fragmented per team, signing keys lack custodians, or compliance wants evidence for legacy services nobody owns.
Project-based DevSecOps programs typically land between USD 30,000 and USD 115,000 depending on repository count, multi-cloud scope, container surface area, and audit reporting depth. Dedicated DevSecOps squads run USD 20,000 to USD 55,000 per month for ongoing gate tuning, supply chain maintenance, and evidence refresh. Senior staff augmentation for DevOps engineers with security depth ranges from USD 7,500 to USD 12,500 per month per engineer on published brackets via hire DevOps engineers. We confirm pricing after discovery once readiness gate answers are documented.
You do. Workflow definitions, policy bundles, signing configs, SBOM storage, and audit evidence templates ship under your IP in your repositories and cloud org. We document how to onboard a new service, rotate signing keys, and regenerate SOC 2 change packets without paging us. Ongoing runtime monitoring can continue through DevOps engineering if you want managed ops after handoff.
Siblings Software coordinates from Miami since 2014. DevSecOps programs default to Eastern and Central business hours for security and platform leads when a gate blocks production, signing keys rotate, or auditors request evidence before customer diligence. Nearshore engineers in Latin America provide depth on pipeline modules, policy-as-code, and supply chain tooling while US stakeholders keep procurement and security review calendars on your side.
Related Services